








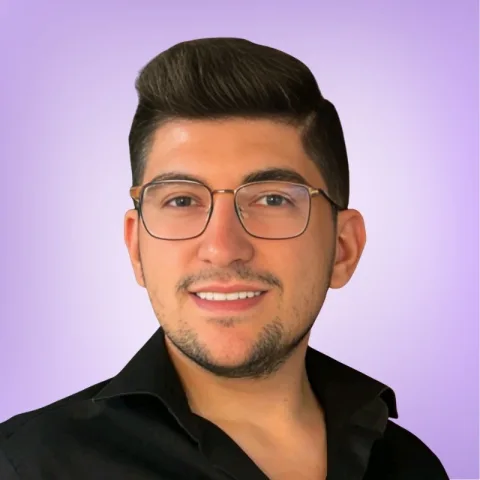
Fatih Yaşar Who is he?
Fatih Yaşar is an Istanbul-based cyber security expert. He delivers solutions focused on security auditing, penetration testing and risk analysis in corporate infrastructures; he builds scalable security systems in the areas of network security, application security and data protection. He aims to protect the digital assets of businesses with security awareness training, incident response and continuous improvement approach.
> Initializing security protocols...
> Scanning network nodes [192.168.1.X]
> Threat detection: 0 Threats Found
> Firewall: ACTIVE
> Inbound Rules: 34 Loaded | Default: DENY
> Outbound Rules: 12 Loaded | Policy: RESTRICTED
> IDS/IPS: ENABLED | Drop Mode: ON
> Encryption: AES-256 Enabled
> TLS Policy: Enforced (TLS 1.2+)
> Key Rotation: Scheduled (Every 24h)
Completed Project
Happy Customer
Years of Experience
Vulnerability Detection
Ransomware and Corporate Security
Ransomware attacks are not just a threat that encrypts files; It is a multi-layered crisis model that targets business continuity, financial resilience and corporate reputation simultaneously. Modern ransomware operations transcend classical antivirus approaches by combining initial access, lateral movement, data exfiltration, and blackmail phases. For this reason, institutions; Early detection, privilege management, backup verification and incident response plans should be designed together. An effective strategy narrows the attack surface, reduces downtime, and sustainably secures data integrity while maintaining regulatory compliance. Particularly for SMEs and critical infrastructures, proactive security architecture prevents costly ransom cycles early.
What is Ransomware? Ransomware is an advanced class of cyber attacks that make data on the target system inaccessible using cryptographic methods and demand payment in exchange for a decryption key, in most cases simultaneously threatening to exfiltrate data; Academically, this model is gizlilik, integrity ve accessibility It is defined as a hybrid blackmail mechanism that simultaneously violates the principles of
Effective protection approach; zero trust, multi-factor authentication (MFA) ve privilege minimization operates its principles together. Segmentation policies that prevent the attacker from escalating from initial access to domain control severely limit ransomware's lateral mobility.
For operational resilience immutable backup, incident response plan ve log correlation is the critical trio. Regular backup fallback testing ensures verification of RTO/RPO targets at the time of actual attack; Central log analysis, on the other hand, reduces the spread of the impact area by catching the anomaly early.
Sustainable success on a corporate scale, vulnerability management, security awareness training ve compliance check depends on the cyclic execution of processes. This framework not only accelerates post-attack recovery; At the same time, it protects brand reputation and customer trust by strengthening compliance with KVKK and sector regulations.
What is Incident Response? Cyber Attack Response Process
Incident Response is the technical, operational and legal response process implemented by an institution after detecting a cyber attack. The goal is not just to stop the attack; The aim is to determine the extent of the damage, prevent the spread, safely restore the system and prevent the same vulnerability from occurring again. Modern cyber attacks, especially ransomware cases, require rapid and planned response.
A cyber attack usually presents with the following symptoms: suspicious network traffic, unexpected user privileges, file encryption, system slowdown, or abnormal activity in log records. The first mistake to make at this point is to panic or shut down the system unconsciously. The correct Incident Response process proceeds in a controlled manner.
How Does the Cyber Attack Response Process Work?
Detection and Isolation: The affected system is separated from the network, preventing spread.
Analysis and Log Review: The source, entry point and domain of the attack are determined.
Pest Removal: Malware or backdoors are removed from the system.
Healing and Security Hardening: Vulnerabilities are closed and security policies are updated.
Reporting and Preventive Plan: A technical report of the process is prepared and a road map is created to prevent it from happening again.
Fatih Yaşar's Incident Response Service Process
As a cyber security expert, Fatih Yaşar carries out the Incident Response process with the methodology of "pre-assessment, planning, implementation, testing and reporting".
In the first stage, the existing infrastructure is analyzed and the scope of the attack is clarified. Then, a risk assessment is made and a technical intervention plan is created. Malware removal, authorization control and closing of security vulnerabilities are implemented step by step. At the end of the process, the system is tested in a controlled manner and all operations are presented in a clear technical report.
The key difference with this approach is that it's not just about cleaning up the attack; is to establish a sustainable security architecture that prevents the same vulnerability from occurring again.
If your organization is experiencing ransomware, data breach or suspicious system activity, a rapid and planned Incident Response process is critical. Correct intervention minimizes data loss and financial damage.
Areas of Expertise
Defense mechanisms specifically designed for your business against the most current threats in the cyber security world.
Fatih Yaşar
Cyber Security Expert
Ransomware Recovery
We implement rapid analysis, isolation and secure return plans in encrypted systems.
Decryption
In appropriate variants, we evaluate the possibility of decryption and restore data access.
Data Recovery
We carry out the process of recovering deleted or inaccessible critical files using forensic methods.
Cloud Security
We establish controls in your cloud architecture that reduce identity, access and configuration errors.
Network Security
We narrow the attack surface with network segmentation, monitoring and rule hardening.
Application Security
We provide vulnerability detection, fixing and secure development support at the web and API layer.
Data Security
Provides protection for sensitive data with classification, encryption and access policies.
Firewall Security
We effectively prevent unauthorized access by optimizing firewall rule sets.
System Reinstallation
We perform clean installation, secure configuration and controlled commissioning after the event.
Strategic Consulting
We plan risk prioritization and sustainable security transformation with an institution-specific road map.
Frequently
asked
Questions
You can find answers to your questions here. Have another question?
Contact me arrow_forward
01
What is Ransomware?
expand_more
02
What is LockBit Ransomware?
expand_more
03
What is Ransomware?
expand_more
04
How Do Ransomware Viruses Work?
expand_more
05
What is Stop Ransomware?
expand_more
06
Is Ransomware a Virus?
expand_more
07
How to Remove Ransomware?
expand_more
08
How Do I Get Rid of Ransomware?
expand_more
09
Which Systems Does Ransomware Target?
expand_more
10
Who is a Cyber Security Expert?
expand_more
Get a Cyber Security Quote Now
Let's plan the most appropriate security approach for your organization together; Let us protect your digital assets sustainably by managing analysis, intervention, improvement and reporting steps in a single flow.